UAE residents have also been cautioned against careless use of VPNs and proxy services, as cybercriminals can exploit intercepted traffic to target users.
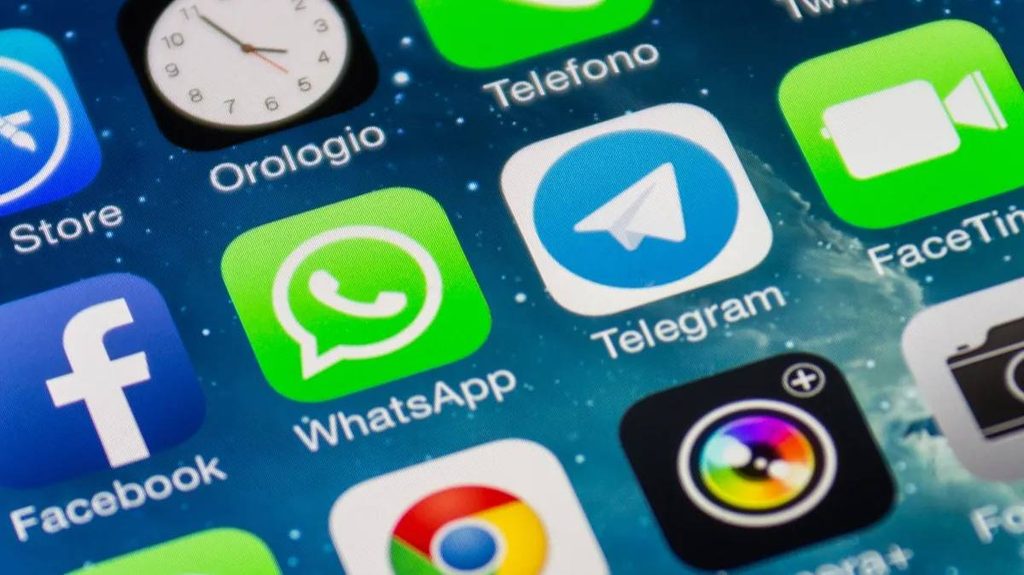
UAE residents are being urged to avoid downloading mobile applications shared through WhatsApp, Telegram and other unofficial channels, as cybersecurity experts warn that such downloads are among the most common — and preventable — ways malware can infect personal devices.
Speaking on the sidelines of GISEC Global 2026, Pushkar Singh, country head for the Middle East and Africa at Protectt.AI, said the UAE records one of the world’s highest volumes of app downloads, making users in the country an attractive target for cybercriminals distributing malicious software disguised as legitimate applications.
“An authentic source means if there is a mobile application on an Android device, it should be downloaded from the Play Store, and if it is an iOS device, from the App Store,” Singh said.
He added that apps distributed through WhatsApp, Telegram or the dark web may have been tampered with or compromised, often without users being aware of the potential security risks before installing them.
Singh said security technology can identify applications that have been downloaded from unauthorised sources or modified after their original release. Such apps can be prevented from functioning even if an employee unknowingly installs them on a corporate device.
He said some applications currently in circulation have been “re-engineered”, with malicious code inserted into otherwise legitimate software. His firm addresses such threats through measures including code obfuscation and runtime protection.
“As a user, they should not be doing it. But enterprises need to build security controls so that even if an unaware user has downloaded it, it should not work,” Singh said.
AI fuelling social engineering scams
Beyond malicious applications, Singh warned of a sharp increase in AI-powered social engineering attacks, with advances in voice and video cloning making impersonation scams increasingly convincing.
He cautioned that transactions apparently authorised during genuine-looking video or voice calls could actually involve fraudsters using AI-generated voices or likenesses to impersonate trusted individuals.
Singh also warned users to be cautious when using VPNs and proxy services without knowing how or where their internet traffic is being routed. Intercepted traffic, he noted, can provide another avenue for cybercriminals to target users.
Fintech growth raises cybersecurity stakes
Singh said the rapid expansion of the fintech sector across the UAE and wider GCC, much of it supported by AI-driven platforms, has made protecting digital transactions increasingly important.
As digital payments continue to grow, securing transactions — from peer-to-peer transfers to enterprise-level payments — has become a critical priority for businesses and consumers.
When it comes to enterprise cybersecurity spending, Singh said businesses are increasingly viewing technologies such as runtime application self-protection and AI security as essential rather than optional, particularly given the financial and reputational damage that can result from a breach.
He advised companies to choose cybersecurity solutions based on their specific requirements rather than focusing solely on cost. Protection, he added, should extend beyond core applications to mobile endpoints and AI agents, where organisations may have less direct control.
“AI is a lot beneficial — it is creating immense efficiencies. But at the same time, there is a darker side, where AI is leveraged to manipulate transactions or create new threat vectors,” Singh said.
AI threats outpacing traditional defences
Singh’s concerns reflected a wider theme at GISEC Global 2026, where CPX chief executive Hadi Anwar told Wam that AI-powered cyber threats are increasing in speed, scale and sophistication, forcing organisations to move beyond traditional security models.
Anwar highlighted deepfake-enabled fraud, identity-based attacks and AI-powered social engineering among the growing threats facing organisations. He also pointed to emerging risks associated with ungoverned AI use, data leakage and the manipulation of AI models.
According to Anwar, generative AI has transformed cybersecurity from a largely technical concern into a broader business and governance issue. This shift requires stronger oversight throughout the AI lifecycle, as well as greater protection for digital supply chains that depend on third-party models.
He cited CPX’s Sovereign Resilience Response, which combines preparedness, protection, automated containment and rapid recovery, as an example of the region’s move towards more proactive and evidence-based cybersecurity strategies.
Secure AI, physical security and operational technology (OT) security were among the areas seeing the strongest demand at this year’s GISEC Global, he added.
Rising supply-chain and phishing risks
Ashraf Koheil, Vice President of Sales for Meta and ANZ at Group-IB, said GCC countries were among the world’s top 10 targets for supply-chain attacks in 2025. He added that phishing attacks targeting the region’s financial services sector accounted for 28.5 per cent of all such attacks across the Middle East and Africa.
Koheil said Group-IB’s “Prediction-First” approach focuses on continuously tracking threat actors, compromised credentials and malicious infrastructure. This intelligence is then combined with AI-powered analysis to identify and flag potential risks before they develop into full-scale security incidents.
Since 2003, the company has conducted more than 1,600 investigations into high-tech crime worldwide. In 2025 alone, it supported 52 law-enforcement agencies globally in operations that resulted in 1,809 arrests and the dismantling of more than 34,800 pieces of malicious infrastructure, he said.
Koheil added that cyber threats increasingly extend beyond an organisation’s own systems, with attackers also targeting suppliers, fintech partners and payment providers. This expanding threat landscape, he said, highlights the growing importance of local expertise and visibility across the wider digital supply chain.