New UAE Rules Aim to Protect Financial Services From System Failures and Cyber Threats.
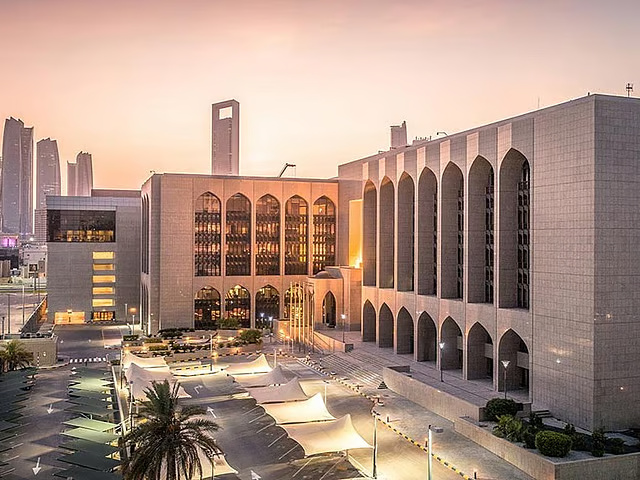
The UAE Central Bank’s new Operational Risk Management Regulation came into effect on September 14, 2026, introducing stricter requirements aimed at ensuring the continuity of services provided by banks and other licensed financial institutions. The framework focuses particularly on risks arising from technology and system failures, cyberattacks, fraud and disruptions involving third-party service providers. It replaces the operational risk management standards and requirements introduced in 2018.
The regulation has direct implications for customers as the use of mobile banking apps, instant transfers, digital wallets and payment cards continues to grow, with more financial services moving to digital channels. Technical disruptions can prevent customers from accessing their accounts, delay transfers and payments or leave payment cards temporarily unusable, making stronger operational safeguards increasingly important.
Stronger Contingency Planning for Financial Institutions
Under the new requirements, which have been circulated to bank management teams, the UAE Central Bank requires financial institutions to establish comprehensive contingency plans and identify “critical operations” whose disruption could significantly affect customers, the institution itself or the wider financial system.
Depending on the nature of each institution’s activities, these critical operations may include:
Critical operations may include:
- Transfers and payments
- Access to customer accounts and salary processing
- The operation of payment cards and other essential financial services
Under the regulation, financial institutions must establish clearly defined disruption tolerance levels for each critical operation. These must specify the maximum acceptable duration of an interruption and the level of impact that can be tolerated before services are restored.
The requirements mark a shift from simply maintaining system recovery plans to demonstrating that institutions can continue delivering essential services, or restore them, within predetermined timeframes and approved impact thresholds.
Boards responsible for oversight and senior management for implementation
The regulation places direct responsibility for overseeing operational risk and resilience on an institution’s board of directors. Boards are required to approve relevant strategies, policies and risk appetite frameworks.
Senior management, meanwhile, is responsible for implementing these measures and ensuring that appropriate systems, resources and qualified personnel are in place to maintain operational resilience.
This means managing service disruptions is no longer treated solely as a technical responsibility for IT departments, but as a broader operational resilience issue requiring oversight across the institution.
The requirements cover information technology risk management and cybersecurity, including the protection of systems and data, vulnerability monitoring, and regular testing of business continuity and disaster recovery plans.
Institutions must also manage the entire lifecycle of an incident — from detection, classification and containment to service recovery, root-cause analysis and the implementation of measures aimed at preventing similar incidents from recurring.
The regulation also requires institutions to promptly notify the UAE Central Bank of any significant deviation from the requirements or any major operational incident. They must also provide supervisory data and reports requested by the regulator.
Financial institutions remain responsible for the security and continuity of their services even when certain operations are outsourced to technology providers, cloud-computing companies or payment-processing firms. Outsourcing does not remove an institution’s regulatory responsibilities.
For customers, the new framework is expected to reduce the frequency and duration of service disruptions, speed up recovery when incidents occur, strengthen data protection and improve institutions’ preparedness for cyberattacks and other operational risks.
However, the regulation does not eliminate the possibility of service disruptions, nor does it automatically entitle customers to compensation for every interruption.
Financial institutions will remain accountable for the security and continuity of their services even when certain functions are outsourced to technology providers, cloud-computing companies or payment-processing firms. Outsourcing does not exempt an institution from its responsibilities to the UAE Central Bank.
For customers, the new regulation is expected to lower the risk and duration of service disruptions, enable faster recovery when problems occur, strengthen data protection and improve financial institutions’ ability to respond to cyberattacks.
However, the new rules do not guarantee that service disruptions will be completely eliminated, nor do they automatically give customers a right to compensation whenever an interruption occurs.